
The Lingering Security Risks of Abandoned Piracy Software
Stevie Bonifield is a dedicated technology journalist specializing in consumer electronics. With a professional background rooted in hardware analysis, gaming trends, and artificial intelligence at Laptop Mag, Stevie provides deep insights into the evolving digital landscape.
The “Netflix of Piracy” Legacy
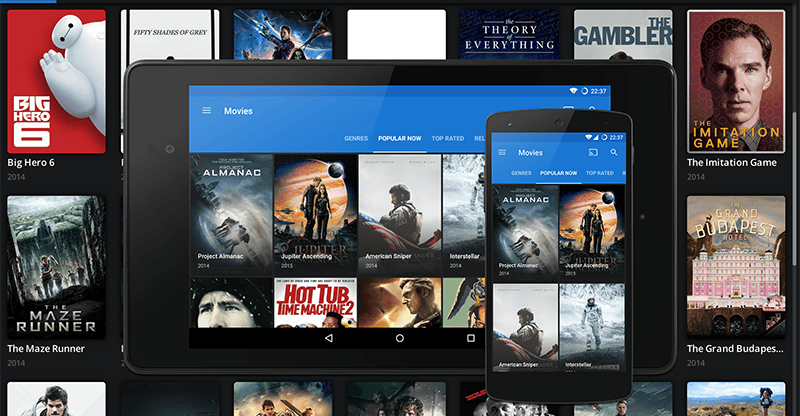
During the mid-2010s, Popcorn Time gained notoriety as the go-to platform for streaming torrented content with a user interface that rivaled legitimate subscription services. While the project officially ceased active development years ago, the software remains a persistent security liability. Millions of users still have the application installed on their computers and mobile devices, unaware that they are essentially carrying a dormant threat.
A Global Botnet Waiting to Happen
Recent investigations by Eye Security have uncovered a troubling reality regarding a specific fork of the software known as “Time4Popcorn.” Despite the project being defunct, the application’s updater continues to operate in the background across Windows, macOS, and Android platforms globally. These devices are constantly attempting to communicate with long-abandoned web domains using unencrypted HTTP protocols, while simultaneously relying on obsolete, vulnerable versions of the Chrome browser.
Why Your Old Apps Are a Liability
Niels Teusink, a researcher at Eye Security, highlights the severe implications of this oversight. Because the updater functions with high-level system privileges, it serves as a potential gateway for malicious actors. By hijacking the abandoned domains, an attacker could easily push unauthorized software to millions of machines, effectively weaponizing them into a massive botnet. Furthermore, the lack of encryption makes these devices susceptible to man-in-the-middle attacks, allowing bad actors to monitor user activity or compromise sensitive data with minimal effort.
This situation serves as a stark reminder that software does not simply “disappear” when it is uninstalled or abandoned; if it remains on your system, it remains a potential entry point for cybercriminals. Users are strongly encouraged to audit their devices and remove any legacy applications that are no longer receiving security updates.