
Bitget Security Breach: The Ongoing Movement of Stolen XRP Assets
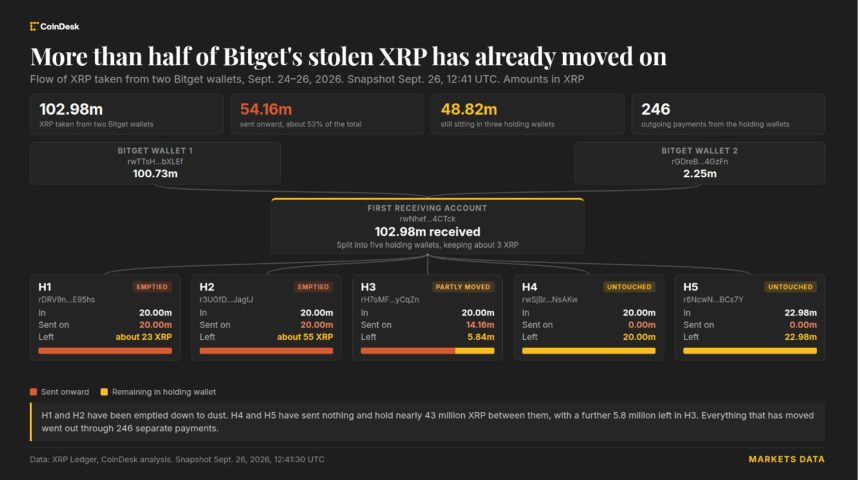
The fallout from the massive $387.5 million security compromise at the Bitget exchange continues to unfold, as the perpetrator behind the attack actively shifts stolen funds. Recent blockchain analysis indicates that approximately $83 million worth of XRP has been transferred out of three primary holding wallets, leaving roughly $75 million still sitting in accounts that remain beyond the reach of current network-level freezing protocols.
Limitations of the XRP Ledger and Asset Recovery
While the crypto community often looks to centralized entities for intervention during hacks, the architecture of the XRP Ledger presents significant hurdles. Although exchanges can proactively blacklist accounts that receive illicit funds, Ripple itself lacks the technical authority to halt transactions originating from wallets directly controlled by the attacker.
This structural limitation highlights the ongoing challenge of asset recovery in decentralized finance. However, some progress has been made in collateral areas: Circle and Tether have successfully intervened by freezing approximately $320,000 in stablecoins linked to the breach, demonstrating that while the XRP itself may be difficult to lock down, the broader ecosystem is attempting to tighten the net around the perpetrator.
Bitget’s Recovery Roadmap and User Protection
In the wake of the incident, Bitget has moved to reassure its user base by confirming that the exchange’s dedicated protection fund will be utilized to absorb the financial impact. The company has emphasized that individual customer balances remain secure and unaffected by the breach.
To restore full functionality, the exchange has outlined a phased recovery plan:
* Withdrawal Resumption: Services will be brought back online in a staggered approach.
* Timeline: The restoration process is scheduled to commence on September 28 and conclude by October 2.
The Scale of the Incident
The breach, which occurred on Thursday, involved the unauthorized extraction of nearly 103 million XRP. These funds were initially fragmented across five distinct holding accounts to complicate tracking efforts. As of Saturday, 12:41 UTC, the attacker’s movement of these assets underscores the persistent threat posed by sophisticated bad actors in the digital asset space. For context, this incident ranks among the most significant exchange hacks of the year, serving as a stark reminder of the importance of robust cold-storage practices and real-time monitoring in the crypto industry.